How MailShrine is priced today (updated October 2026): MailShrine is an email suite, not a single flat-fee product. Live: Email Marketing, Business Email, AI Email Lead Generator, Email Sanitization (200 credits per month, refilled every month), and Developer API — Live. In development: Email Automation only. Email Marketing, Email Lead Generator, and Developer API use pay-as-you-go credits (1 credit = 1 email, harvested lead, or API send), with monthly Email Marketing options. Stored contacts do not raise the bill. Business Email is billed by mailbox. Products and plans are differentiated — not every feature lives on every plan. Confirm live packs on Pricing.
If you are a B2B sales leader or agency owner building a cold email infrastructure, the first roadblock you hit is the technical hurdle of sending thousands of emails efficiently.
Historically, developers solved this by spinning up massive transactional SMTP (Simple Mail Transfer Protocol) servers via platforms like Mailgun, SendGrid, or Amazon SES.
While SMTP architecture is perfect for sending 100,000 password reset emails to existing users, using SMTP for cold B2B outreach in 2026 is incredibly dangerous. It is the fastest path to getting your domain permanently blacklisted by Google Postmaster.
This technical guide breaks down exactly why legacy SMTP routing triggers modern spam filters, and why many outreach teams now send from their own inbox (or a Cloud path they control) instead of a transactional relay.
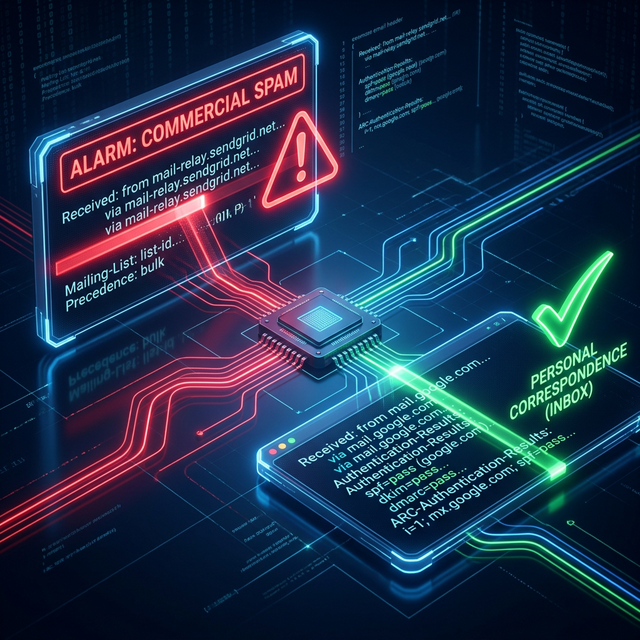
The Technical Founder Scenario: "The Linda Header Audit"
Meet Linda, a CTO at an AI startup. She is sending her outreach through a standard SendGrid SMTP relay.
- The Confusion: She’s frustrated that her open rates are stuck at 12%, even though she spent weeks cleaning her list.
- The Audit: She performs a "Header Audit" on her sent messages.
- The "Ah-ha" Moment: Inside the metadata, she sees a tiny tag:
via sendgrid.netandX-SG-EID. To Gmail's filters, this is a giant red flag that says "THIS IS BULK MAIL." - The Solution: She switches to MailShrine and sends from her connected Gmail inbox (or MailShrine Cloud with a verified domain). The bulk-relay
viatag disappears on inbox sends. Her open rates jump to 48% within 10 days.
Linda's "API-Sent" Email Draft:
"Hey {first_name}, I checked your API documentation. I think we have a better way to handle those Webhooks. Free to chat for 15 minutes?"
Linda realized that using the wrong "pipe" was the reason her emails were being treated like spam.
1. The Anatomy of an SMTP Relay
Let's look at what happens when you use an SMTP service (like SendGrid) to send a cold sales email.
When you dispatch the campaign, the email does not leave your actual Google Workspace or Microsoft 365 server. Instead, your software hands the email packet over to SendGrid's centralized server farm. SendGrid then attempts to deliver the payload to your prospect's inbox on your behalf.
The Problem: Signature Flags
Google and Microsoft's spam algorithms do not just read your subject line. They analyze the metadata headers of the envelope. When an email arrives via SMTP, the headers explicitly state: Sent from you@yourcompany.com via sendgrid.net.
The moment a corporate spam filter sees a bulk-relay signature like via mailgun or via sendgrid on a cold email to a recipient who did not opt-in, it instantly categorizes the email as a "Commercial Broadcast." The email is aggressively scrubbed, and in 90% of cases, routed directly to the Spam or Promotions folder.
2. The Shared IP "Neighborhood" Disaster
Beyond the metadata footprint, SMTPs operate on shared architecture.
When you sign up for a $35/month Mailgun account, you are placed on a shared outgoing IP address alongside perhaps 5,000 other businesses.
- What happens if three of those businesses are bad actors sending crypto scams?
- What happens if one of them is an amateur marketer who blasted a purchased list of 50,000 dead emails, generating massive hard-bounce rates?
The entire IP address is burned. Because your legitimate B2B sales pitch is exiting from that exact same burned IP address, you absorb the collateral damage. Your domain reputation is tarnished by association.
Note: You can purchase a Dedicated IP from an SMTP provider, but it begins with a completely zeroed-out reputation score. The moment you push high volume through a fast-tracked dedicated IP, firewalls flag it as a "Snowshoe Spam Attack."
Header Audit: What Spam Filters Actually See
When you send an email via an SMTP relay (Mailgun, SendGrid), your email technically arrives with a "Via" header. Here is a simplified version of the code snippet that Google's algorithm flags:
text Received: from mail-relay.sendgrid.net (relay.sendgrid.net [167.89.x.x]) X-SG-EID: 123456789... X-Entity-ID: abcdefg... List-Unsubscribe: <mailto:unsubscribe@sendgrid.net>
The Result: Even if your copy is perfect, the presence of X-SG-EID and the via sendgrid.net tag tells Gmail: "This is commercial mass mail."
The MailShrine inbox-send difference: When you send through a connected Gmail or Microsoft inbox (OAuth), the header looks like a normal mailbox send — not a Direct-Inbox API product and not a transactional relay:
text Received: from mail-wm1-x11.google.com (mail-wm1-x11.google.com [2a00:1450:4864:20::12c]) Message-ID: <...your-custom-id@gmail.com> Authentication-Results: spf=pass, dkim=pass, dmarc=pass
No "Via" tags. No bulk headers. Just 1-to-1 human correspondence.
3. The New Standard: Inbox Sending (and Cloud when you need it)
If transactional SMTP is a poor fit for cold outreach, how do teams scale volume? Many send from connected inboxes; others use MailShrine Cloud for hosted campaigns.
MailShrine is a credit-based suite, not a “Direct-Inbox API” product. Inbox sends use your Gmail / Microsoft / Yahoo / Custom SMTP connection. Cloud sends use MailShrine-hosted infrastructure. Both spend 1 credit per email.
The Technical Simulation of Human Behavior
When MailShrine sends via a connected Gmail inbox, it can construct the message in that mailbox's Sent folder so receiving filters see a normal personal send — not a via sendgrid relay. MailShrine Cloud is a different, hosted path for campaigns that need Cloud tracking.
To the receiving server, this is completely indistinguishable from you sitting at your laptop, manually typing an email to a friend, and clicking send.
There is no via sendgrid metadata. There are no shared IP bad neighborhoods.
Inbox sends inherit that mailbox’s existing SPF / DKIM / DMARC authentication. That is not a cryptographic uniqueness guarantee, and MailShrine Cloud is a separate hosted path.
Horizontal Scaling
Provider sending limits still apply (Google typically allows on the order of ~50-100 cold emails per day per inbox), so modern outreach uses horizontal scaling.
Instead of routing 5,000 emails through one massive SMTP pipe, modern teams purchase 10 subset domains (e.g., trycompany.com), create an inbox for each, and connect those inboxes in MailShrine Email Marketing. You then spread the 5,000 emails across isolated mailboxes you control. MailShrine is not an “intelligent rotation engine” product and not a Direct-Inbox API.
When SMTP IS the Correct Choice
For balance: SMTP relay infrastructure remains essential for transactional emails. If you are building an application that sends:
- Password reset confirmations
- Order receipts and shipping notifications
- Two-factor authentication (2FA) codes
- System alerts and security warnings
… then SendGrid, Mailgun, and Amazon SES are excellent, purpose-built tools. These are emails to existing users who explicitly expect them.
The critical mistake is using that same transactional pipe for cold B2B outreach — a completely different use case that needs a send path you control (your inbox or MailShrine Cloud), not a shared transactional relay.
2026 Policy Update: Google & Microsoft DMARC Enforcement
As of February 2026, both Google and Microsoft have tightened their DMARC enforcement policies for bulk senders:
- Senders dispatching 5,000+ emails/day must have a fully published DMARC policy with at least
p=quarantine. - Emails failing SPF or DKIM alignment are now rejected (not just flagged) by default.
- The "via" tag from SMTP relays now carries a heavier negative weight in spam scoring algorithms.
This makes authenticated sending from a domain you control (inbox or verified Cloud) — where SPF, DKIM, and DMARC can pass — more critical than ever.
Conclusion: Protect Your Domain
Transactional SMTP servers remain critical infrastructure—for transactional emails. Use them for your application's 2FA codes, shipping receipts, and welcome payloads.
However, the moment you attempt to use those centralized vectors to initiate cold conversations with new prospects, you are triggering alarms across every major corporate firewall on the internet.
Modern B2B revenue needs sending that does not look like a transactional blast from a shared relay.
Citations & References
- Reference: SendGrid: Understanding Shared vs Dedicated IPs
- Reference: Postmark: The difference between broadcast and transactional email
Written by Alexander P., Systems Architect. Alexander routinely audits massive outbound email infrastructures for Series-A startups, migrating them off legacy SMTPs to secure, scalable API workflows.